
NullRun
Runtime Authorization for AI Agents - Before They Execute
6 followers
Runtime Authorization for AI Agents - Before They Execute
6 followers
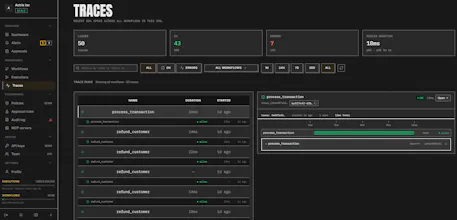
NullRun is a runtime authorization layer for AI agents. It evaluates and enforces every agent action against your policies, including tool use, budgets, and MCP operations: allow, require human approval, or block. Every decision is recorded as auditable evidence, giving teams control over agent execution and a governed path to AI adoption. Python SDK, hosted control plane, RBAC, human approvals, traces, audit trail, and tenant isolation are live. Self-serve and deploy in minutes.
Interactive



Free Options
Launch Team / Built With


Hey Product Hunt 👋 I'm Anatolii, the solo founder behind NullRun.
I didn't start with a big "AI governance" thesis.
I started with a much more annoying engineering question: if an agent is allowed to use a tool, who actually gets the final say when it's time to execute?
NullRun sits right at that execution boundary - a control point that checks an agent's tool call before it actually runs, instead of trusting the agent to decide for itself. The first version was literally a Python decorator around one function. I kept pushing the same idea closer to the real point of execution until it became a product.
What interests me now isn't whether agents can make mistakes - we already know they can.
It's what happens when an agent has enough access for a mistake to actually matter.
I'm also building this solo, so I'd genuinely rather learn from people here than just talk about what I built.
If you're working with agents: what's one action you'd trust an agent to request, but still wouldn't trust it to execute on its own? Real cases welcome, especially the messy ones.