Everyone is obsessed with how fast tools like Cursor, Claude Code, Replit and Lovable let you ship apps.
But almost nobody is asking the obvious question: Can your users see someone else's data?
Most vibe-coded apps have thousands of permission combinations across roles, APIs, pages, and databases. AI is great at building features, but it doesn't automatically guarantee that every authorization check is correct.




Congrats on the launch this is such a timely product given how fast vibe coding tools are scaling without security guardrails. Curious, when your platform finds and fixes vulnerabilities automatically how do you handle edge cases where a fix could break existing app logic? Is there a approval step before changes go live?
Release AI
@aymi_malik
Thank you! And great question. Yes, there's always an approval step. We never push changes to your app ourselves.
Here's the flow: Perfai finds the issue, shows you proof of how we exploited it, and writes a suggested fix with full context. Your developer (or your AI coding tool) reviews and applies it. If you built with Replit, Lovable, or Cursor, you can run "Fix all Perfai issues" and your coding agent applies the fixes, but you still review before deploying.
We keep a human in the loop on purpose. Access control changes can break real user flows if applied blindly, exactly the edge cases you're describing. After you apply a fix, just re-run the test. Perfai verifies the issue is gone and your other permission checks still pass. Drift detection also keeps testing as your app changes, so if a fix causes a new gap later, you'll catch it.
The live vulnerabilities in vibe apps angle is useful, but I would want to know where the fix boundary is. Does Perfai mostly generate a patch suggestion, or can it prove the vulnerable path is no longer reachable after the one-prompt fix? That verification loop is where these tools usually get messy.
Release AI
@xiaosong001
Here's the reply with the loop framing:
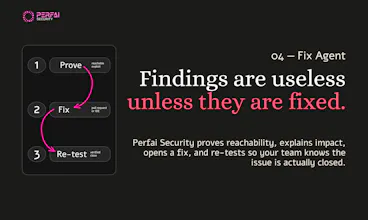
Great question! Perfai works in a simple loop: Test, Fix, Retest.
Test: enter your app URL and our agents test your live app like a real pentester. Fix: say "Fix all Perfai issues" or "Fix critical Perfai issues" in Replit, Lovable, or any code agent, and it instantly generates the fixes for you to review. Retest: say "run security" and Perfai retests your live app to confirm issues are fixed and nothing is broken.
So the proof is a real retest against your running app, not just a code diff. We also do drift detection, so every release gets tested for new gaps.
Every finding comes with proof in a pentest-style report. There's a free tier if you want to try it, and I'm happy to share a 50% discount code plus extra credits. Ping me if you need help onboarding!
For apps built on Lovable or Replit specifically, where the developer often doesn't have direct access to the underlying infrastructure or can't freely modify server-side auth logic, how does Perfai actually apply fixes? Those platforms have constraints on what you can change and where, curious whether the "1-prompt fix" works within those constraints or requires exporting the project first.
Release AI
@ansari_adin
Great question! No export needed. The fixes work within the platform itself.
Perfai doesn't touch your infrastructure. When you say "Fix all Perfai issues" in Lovable or Replit, the platform's own AI agent generates the fixes in your app code, the same code you already own and can edit there. Most access control gaps in vibe-coded apps live in that app layer, like missing auth checks on API routes or client-side-only permission logic, so they're fixable right inside the platform.
After you review the fixes, say "run security" and Perfai retests your live app to confirm the issues are fixed and nothing is broken. Test, Fix, Retest.
Every finding comes with proof in a pentest-style report. There's a free tier if you want to try it on your own app, and I'm happy to share a 50% discount code plus extra credits. Ping me if you need help onboarding!
Perfai Security
Hi @thys_beesman , thanks for asking. Perfai Security offers both, and this is where Perfai Security really shines. We don't just stop at a list of vulnerabilities.
We ship an MCP server (perfai-mcp-server) you drop into your IDE (Cursor, VS Code, or any MCP-compatible agent). Once connected, it pulls your reported issues directly into the editor, and for any issue it generates a context-rich fix prompt with exact endpoint, vulnerability, remediation contexts. Your IDE's coding agent then implements the fix right in your codebase, following your existing patterns and architecture.
We deliberately keep the developer in the loop rather than auto-patching your repo. This way, we never require any code-access. And so the fix lands in your editor where you review and merge it like any other change.
So it's detection → guided remediation → fix, without Perfai Security ever writing to your code behind your back.
TL;DR — Perfai Security maps your app, detects vulnerabilities, provides the fixes, and then retests to verify the issues are patched.
Release AI
@thys_beesman
Great question! Both. We detect and fix.
Every finding comes with an instant fix you can apply with one prompt in your code agent, like "Fix All", "Fix Critical", or "Fix #2". You don't need to be a security expert or spend hours figuring out how to patch each issue yourself. The Fix Agent hands you exactly what to do.
That's the full loop: our agents test your live app across UI, API, data, and roles, find the gaps, and give you one-prompt fixes. And with drift detection, we catch new issues as your app changes, so you're never relying on a stale report.
All this without paying thousands for a pentest. You get a full pentest-style report on the free tier at perfai.ai. We're also giving away 50% discount codes for the launch. Need extra credits or help onboarding your app? Just reach out. Happy to help!
Faster than a manual pentest sure, but does it catch the weird edge cases a human would?
Perfai Security
@trevor_nicholas2 honest answer: if a manual pentester checks ~50 permission combinations before the clock runs out, Perfai Security tests all 6,000+ (across every role × data × action) ...including the weird ones, including chained privilege escalation, cross-tenant ownership quirks, admin functions live under a hidden route. These "edge cases" are usually just cases nobody had time to reach by hand, but in practice, we've surfaced findings a decade of manual pentests had missed. Where a creative human still shines is open-ended business logic, and we're pushing into that too.
Release AI
@trevor_nicholas2
Fair question, and the honest answer is: humans and machines catch different things.
A skilled pentester might spot a weird one-off flaw with creativity. But humans have limited time. They test for a few days, sample some endpoints, and move on. Our agents test everything: every role against every data type and action, thousands of combinations a human would never have time to try. Weird edge cases often live exactly in those untested combinations.
And here's why our focus matters: Gartner reports that access control issues account for about 50% of breaches and security incidents. That's precisely what we go deepest on. In total we cover 75+ AI-threat categories, spanning access control, auth, and classic categories.
Plus a pentest is a snapshot. With drift detection, we keep testing as your app changes, so you're covered next month too, not just today.
Try it free at perfai.ai and get a full pentest-style report. We're giving away 50% discount codes for the launch too. Need extra credits or help onboarding your app? Just reach out. Happy to help!
Voquill
Congratulations! Does this work with any deployed web app, or is it mainly built for apps created with AI coding tools?
Perfai Security
@henry_habib It works with any deployed web app that has a URL. We test black-box from the outside, so we're fully stack-agnostic. It doesn't care whether you hand-wrote it, vibe-coded it, or inherited it. The "vibe-coded" framing is where our solution is needed most right now, but the engine tests any app with roles, APIs, and a database. The only place the AI-coding tool matters is the fix handoff... our Fix Agent delivers remediation through an MCP server you drop into any IDE (Cursor, VS Code, Claude Code…), and it works even if you just want the exact patch to apply yourself. Point it at any URL and see. You can sign up for free or get 50% off our pro plan using the discount code (in pinned comment).
Release AI
@henry_habib
Thank you!
It works with any deployed web app. If it runs in a browser and has a URL, we can test it. Doesn't matter if it was built by AI agents, a dev team, or ten years ago by a contractor nobody remembers.
We talk a lot about vibe-coded apps because they're the most at risk: shipped fast, often with no security review, and full of access control gaps. But the testing itself doesn't care who wrote the code. Our agents test the running app across UI, API, data, and roles, so any stack works: React, Rails, PHP, whatever.
Same simple flow for everyone: paste your URL, our agents explore, sign up their own test accounts, and get to work. Drift detection keeps coverage fresh as the app changes.
Try it free at perfai.ai and get a full pentest-style report. We're giving away 50% discount codes for the launch too. Need extra credits or help onboarding your app? Just reach out. Happy to help!
Great concept. My team runs into this problem consistently. Even with AI guardrails and instructions, we have to spend valuable hours testing for vulnerabilities.
Release AI
@zohaib_akmal
Thank you! Your team's experience is exactly why we built this. AI guardrails help, but they can't replace real testing, and doing it by hand eats hours.
Perfai Security does that testing for you. Just enter your app URL. Our agents sign up their own test accounts, then test thousands of permission combos across roles and actions. You get a pentest-style report with proof for every issue. We also run drift detection, so new gaps get caught as your app changes.
Try it free at perfai.ai. Use code PHLAUNCH50 for 50% off any paid plan. If your team wants extra credits or onboarding help, just message me!